Key Takeaway: Information gaps weaken your cybersecurity strategy because you cannot protect what you cannot clearly see or understand. When asset inventories, access records, monitoring coverage, or ownership details are incomplete or inconsistent, decision-making slows and risks are misjudged. Strengthening your cybersecurity strategy starts with improving visibility, aligning teams around shared facts, and ensuring that critical systems, data, and responsibilities are clearly documented and understood.
The Missing Pieces That Change Everything
Your cybersecurity strategy can fail for a simple reason: you do not have the right information. You can have a solid security plan, a sensible defense roadmap, and a thoughtful risk-management approach. Yet small gaps in knowledge still derail outcomes.
If that sounds abstract, think about how you make any important decision. You would not plan a trip with half a map. You would not budget with missing invoices. Cybersecurity works the same way. When your teams lack clear, shared facts, they make confident choices on shaky ground.
This topic matters because modern organizations move fast. They adopt cloud services, connect partners, and support remote work. Each change adds complexity. Complexity creates blind spots. Those blind spots quietly weaken your ability to prevent problems and respond well.
You might even recognize the feeling. “We bought the right tools, so why do we still feel exposed?” That question usually points back to information gaps.
How Information Gaps Derail a Cybersecurity Strategy
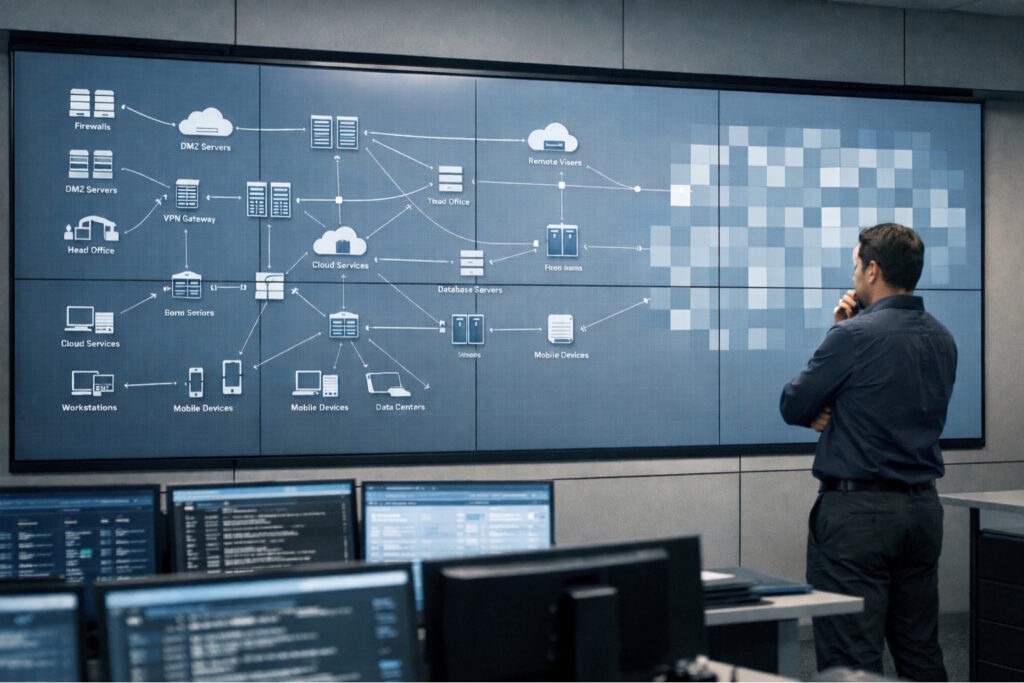
A cybersecurity program depends on visibility. You need to know what you own, how it connects, and who can touch it. When you lack that clarity, your cybersecurity strategy becomes a set of assumptions.
Assumptions create two costly patterns. First, teams chase the wrong priorities. Second, they miss the risks that matter most. Neither problem requires sophisticated attackers. Confusion does the damage on its own.
What counts as an information gap?
An information gap is not only “missing data.” It can also be stale, scattered, or inconsistent information. It shows up when people cannot answer basic questions with confidence.
Here are a few common examples:
- You do not have a reliable inventory of devices, applications, and cloud resources.
- You cannot tell which systems store sensitive data, and which teams own them.
- You do not know who has access, especially after role changes or reorganizations.
- Your monitoring does not cover key systems, so alerts tell only part of the story.
- You depend on vendors, but you lack a clear view of their security posture.
None of this sounds dramatic. That is the point. These gaps feel routine until an incident forces urgent decisions.
The everyday moments where gaps cause real harm
Information gaps rarely announce themselves. They appear during normal work, when decisions pile up.
Imagine a simple scenario. A critical vulnerability makes the news. You want to patch quickly. Your team asks, “Which servers run that software?” If the answer depends on guesswork, you lose time. You also lose confidence.
Now consider a different situation. A user reports suspicious activity. The help desk needs context. Which device is involved? Which login looks unusual for that person? Which systems matter most to the business today? If those answers live in five tools and three inboxes, response quality drops.
These problems grow when organizations change. Mergers and acquisitions add new systems. Teams shift responsibilities. Contractors come and go. Cloud accounts multiply. Over time, the “official” picture drifts away from reality.
When that happens, your strategy may look strong on paper. In practice, it becomes hard to execute.
Questions to ask before you update your cybersecurity strategy
If you want to pressure-test the quality of your plan, start with questions that sound almost too basic. These are the questions leaders ask.
- “Do we know what we need to protect most?”
- “Can we name the systems that would hurt us if they failed?”
- “Do we know who owns each critical system?”
- “Can we quickly tell who has access to sensitive data?”
- “Do we trust our monitoring coverage, or do we hope it is enough?”
- “Could we explain our risk posture in one page, without hedging?”
If these questions spark debate, you have found useful signal. Debate often means the truth sits in fragments.
Why More Tools Rarely Fix the Visibility Problem
It is tempting to respond to uncertainty with more software. Tools matter, but they do not solve the human problem of alignment. They also do not guarantee clean inputs. Many organizations end up with “tool sprawl.” Each system generates data in a different format. Each team uses its own dashboards. The result is not clarity. It is noise.
This is how information gaps survive in well-funded environments. The organization owns plenty of data. Yet no one can turn it into a shared, trusted picture. If you have ever thought, “We have reports everywhere, but no answers,” you already understand the issue.
Making Information Flow a Normal Part of Security Work
You do not need perfection to make progress. You need habits that improve the completeness and consistency of what people know. A helpful way to think about this is to focus on “decision-grade information.” In other words, can your teams make good choices quickly with what they have?
Start where business impact is obvious
Many security efforts stall because they start too broadly. A better approach begins with what the business cannot afford to lose. That might be customer data, payment systems, production operations, or core intellectual property.
Once you agree on what matters most, visibility work becomes less theoretical. People engage when the stakes feel real.
Clarify ownership, not just technology
Information gaps persist when responsibilities stay fuzzy. If no one “owns” a system, no one maintains its documentation. If access requests route through informal channels, access records become unreliable.
Ownership does not need bureaucracy. It needs a short, clear answer to “Who is accountable for this?” That single point of accountability improves the quality of information over time.
Treat third parties as part of your environment
Many modern organizations run on partners. Vendors host applications. Contractors access systems. Service providers manage infrastructure. That reality expands your risk boundary.
A practical goal is not to interrogate every supplier. It is to know which suppliers matter most, and what you would do if one had a security issue. That stance turns vendor risk from vague worry into manageable planning.
Conclusion: Turning Unknowns into Momentum
A strong cybersecurity strategy depends on shared facts, not heroic effort. When your organization closes information gaps, you gain speed, confidence, and better decisions. You also reduce the chance that a routine issue becomes a high-impact event.
Conversations about visibility, governance, and digital risk are evolving quickly. At Tech Scope Connect, we explore how leaders approach these challenges through expert discussions, live broadcasts, and global summits focused on emerging technology. Join the conversation and stay engaged as the future of cybersecurity strategy continues to evolve.